CodeThreat vs Codacy Quality
Dive into the comparison of CodeThreat vs Codacy Quality and discover which AI Code Assistant tool stands out. We examine alternatives, upvotes, features, reviews, pricing, and beyond.
In a comparison between CodeThreat and Codacy Quality, which one comes out on top?
When we compare CodeThreat and Codacy Quality, two exceptional code assistant tools powered by artificial intelligence, and place them side by side, several key similarities and differences come to light. Neither tool takes the lead, as they both have the same upvote count. You can help us determine the winner by casting your vote and tipping the scales in favor of one of the tools.
Don't agree with the result? Cast your vote and be a part of the decision-making process!
CodeThreat


What is CodeThreat?
CodeThreat scans repositories for vulnerabilities in source code, open-source dependencies, infrastructure templates, and leaked secrets. Rule-based SAST covers 1,740+ security rules across 27+ languages, while AI agents filter false positives, review pull requests, and map repository structure. SCA runs through Trivy and Syft across 15+ package ecosystems, and IaC scanning covers Terraform, Kubernetes, and Docker with checks mapped to CIS, NIST, ISO 27001, and SOC 2.
Most SAST vendors hand developers a long alert list and leave triage to the team. CodeThreat's false positive elimination agent re-checks rule-based findings with semantic reasoning and suppresses non-exploitable alerts before they hit the dashboard. Each eliminated finding gets a short explanation of why it was dropped, which is rare in scanners that treat AI as a marketing label rather than a filter step in the workflow.
DevSecOps teams connect GitHub, GitLab, Bitbucket, or Azure DevOps repos so scans trigger on every pull request and push. Security engineers get SAST, SCA, secrets, and IaC coverage in one platform instead of stitching four separate tools. Small teams can start on the free tier with three private repos; scaling teams move to per-contributor Pro billing at $39 per month.
Codacy Quality
What is Codacy Quality?
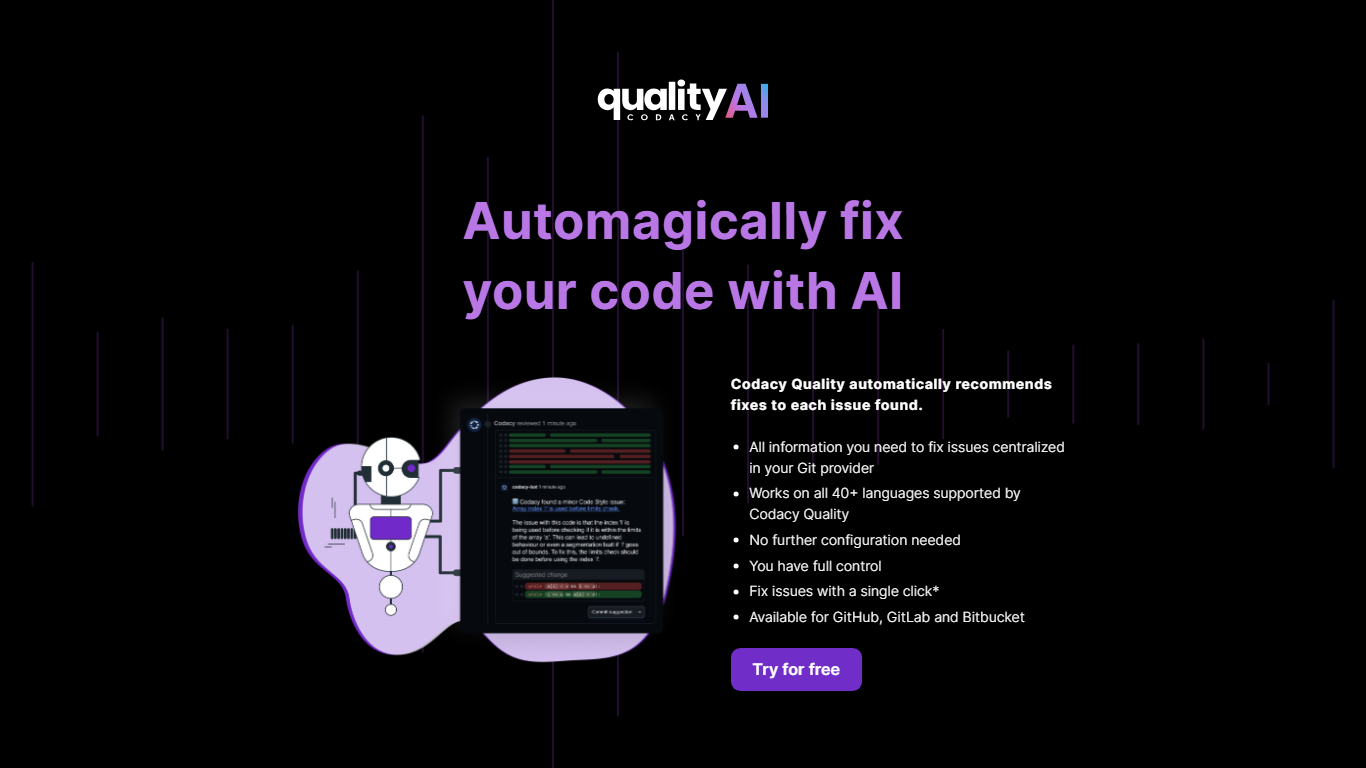
Codacy Quality scans AI-generated and human-written code for security flaws, quality regressions, and policy violations before changes merge. It plugs into GitHub, GitLab, and Bitbucket pull requests, plus VS Code, JetBrains, and Cursor, so fixes surface inside the tools developers already use instead of in a separate dashboard nobody checks.
Where generic linters stop at style rules, Codacy Quality layers SAST, secret scanning, dependency (SCA) checks, infrastructure-as-code rules, and AI-specific guardrails that flag unapproved model calls or policy violations from agent-generated code. Its AI Reviewer adds low-noise pull request comments with ready-to-commit fix suggestions, which matters when teams ship faster with copilots but still need audit-ready evidence.
Engineering leads, security teams, and platform groups at mid-market and enterprise companies use it to standardize coding standards across dozens of languages without assigning someone to babysit every repo. Open-source projects can run it free forever, while private teams start with a 14-day trial and no credit card.
CodeThreat Upvotes
Codacy Quality Upvotes
CodeThreat Top Features
1,740+ SAST rules across 27+ languages including Python, Java, Go, and C#
Free plan includes 5 AI PR reviews and 10 false positive elimination runs per month
SCA matches versions against NVD, GHSA, and OSV databases via Trivy and Syft
IaC scanning covers AWS, Azure, GCP, and Kubernetes with 500+ security checks
Pro plan costs $39 per contributor per month with unlimited private repositories
Integrates with GitHub, GitLab, Bitbucket, and Azure DevOps for CI/CD pipelines
Codacy Quality Top Features
Scans 49 programming languages with shared coding standards across repositories
AI Reviewer leaves pull request feedback with one-click fix suggestions on GitHub, GitLab, and Bitbucket
Codacy Guardrails runs SAST, SCA, and secret scans inside VS Code, JetBrains, and Cursor as you type
Supports up to 100 private repositories on the cloud-hosted starter tier with unlimited lines of code
Daily CVE and malicious package re-scans keep dependency risk current across legacy codebases
AI Risk Hub enforces org-wide AI coding policies such as unapproved model calls and prompt-injection checks
CodeThreat Category
- Code Assistant
Codacy Quality Category
- Code Assistant
CodeThreat Pricing Type
- Freemium
Codacy Quality Pricing Type
- Freemium